
Enlist various functions of protocols of SSL.
- […] functions of protocols of ssl : https://www.doubtly.in/q/enlist-functions-protocols-ssl/ […]
- […] functions of protocols of ssl : https://www.doubtly.in/q/enlist-functions-protocols-ssl/ […]
Secure Socket Layer (SSL) provides security to the data that is transferred between web browser and server. SSL encrypts the link between a web server and a browser which ensures that all data passed between them remain private and free from attack.
Secure Socket Layer Protocols:
In the SSL Record Protocol application data is divided into fragments. The fragment is compressed and then encrypted MAC (Message Authentication Code) generated by algorithms like SHA (Secure Hash Protocol) and MD5 (Message Digest) is appended. After that encryption of the data is done and in last SSL header is appended to the data.
Handshake protocol uses four phases to complete its cycle.

Change-cipher protocol consists of a single message which is 1 byte in length and can have only one value. This protocol’s purpose is to cause the pending state to be copied into the current state.
This protocol is used to convey SSL-related alerts to the peer entity. Each message in this protocol contains 2 bytes.
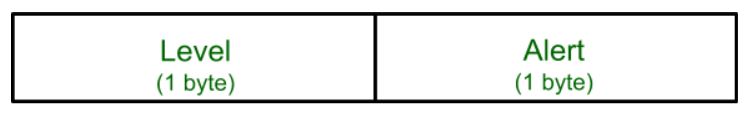
The level is further classified into two parts:
Warning (level = 1):
This Alert has no impact on the connection between sender and receiver. Some of them are:
Bad certificate: When the received certificate is corrupt.
No certificate: When an appropriate certificate is not available.
Certificate expired: When a certificate has expired.
Certificate unknown: When some other unspecified issue arose in processing the certificate, rendering it unacceptable.
Close notify: It notifies that the sender will no longer send any messages in the connection.
Unsupported certificate: The type of certificate received is not supported.
Certificate revoked: The certificate received is in revocation list.
Fatal Error (level = 2):
This Alert breaks the connection between sender and receiver. The connection will be stopped, cannot be resumed but can be restarted. Some of them are :
Handshake failure: When the sender is unable to negotiate an acceptable set of security parameters given the options available.
Decompression failure: When the decompression function receives improper input.
Illegal parameters: When a field is out of range or inconsistent with other fields.
Bad record MAC: When an incorrect MAC was received.
Unexpected message: When an inappropriate message is received.
Reference : https://www.geeksforgeeks.org/secure-socket-layer-ssl/
Log in or create a free account to answer this question.
